Focus Topics
We are closer to AI regulation than we think
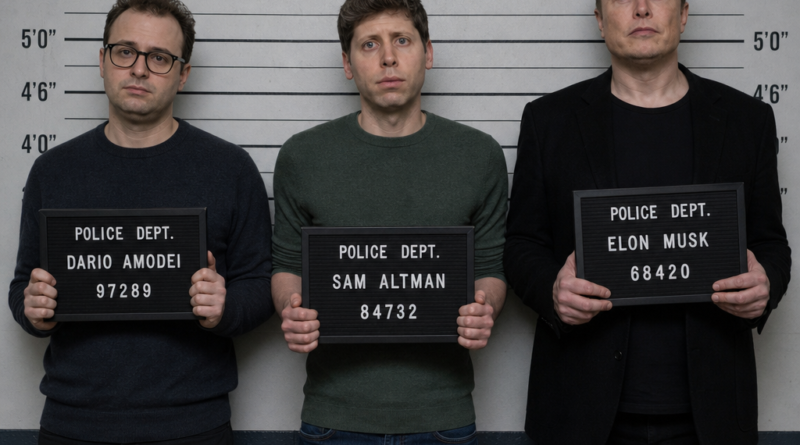
Regulating AI is a major issue in government halls worldwide, but legislators’ distinct lack of technical competence is hampering the effort. A less technical solution may exist. It has existed for more than a century; it requires little or no further legislation, and it could result in criminal charges against the CEOs of AI platforms.
(Note: senior executives at AI companies including Anthropic, Open AI and C3 AI were contacted for comment. None responded to the requests.)
TL;DR
License AI use like cars
Holding companies responsible
Groundwork already laid
Doctrine of reasonable care
Let’s begin with automotive use. Virtually every country requires licensing of drivers and registration of vehicles.

Baby bust is forcing a rethink of AI hype
When AI burst upon the scene a few years ago, it became a boon to the cybersecurity industry. The AI sector pushed a narrative that AI was not just a tool, but a way to replace human workers. Cyber threats exploded and there was greater demand for tools and services. The security industry glommed onto that narrative with AI-driven services. That had the expected result of destroying any goodwill available to AI technology.
However, recent revelations about the effectiveness of AI replacements are making proponents change their tune. What changed? Let’s start with human fertility.
The security gap everyone should be talking about
Most businesses and the MSPs who support them have built a reasonably solid security stack. Email filters catch most phishing attempts before they land. Endpoint tools monitor devices around the clock. Security awareness training teaches employees what to watch for. For most organizations, that covers the obvious bases.
Scam Bucket: You can escape Meta Hell
Not all scams take money from you. One of the biggest security scams is the belief that once you have joined a Meta platform, it is impossible to leave. The news the Meta is working with a government contractor to make facial recognition tech for ICE agents has accelerated interest in how to escape Meta Hell. The question is, how?
Migration from Meta platforms is no longer a niche trend. Through 2025 and 2026 there is a sustained structural shift in the social media. Just consider the explosive growth of Bluesky, which closed 2025 with over 41.4 million registered users, a 60% year-over-year increase, with daily active users climbing past 4.5 million. That represents real growth from status into mainstream viability.
Will Mythos & Glasswing End the Zero-Day Era as We Knew It?
For decades, cybersecurity strategy has revolved around a shared assumption: zero-day vulnerabilities are rare, expensive to find, and difficult to exploit at scale. That assumption is now breaking down. The emergence of Mythos, the advanced AI system developed by Anthropic, marks a turning point in how vulnerabilities are discovered, weaponized, and defended against—and it forces security leaders to rethink long-held priorities.
Analysis: Trump’s EO revives lethargic PQC sector
The Trump regime’s latest executive order (EO) last week is a shot in the arm to the moribund Post-Quantum Cryptographymore
Internet of Things

Security concerns reach beyond CISOs
The English riots this past week provide a Dickensian “best of times…worst of times.” context to politics in the United Kingdom and possibly the United States later this year. The UK has had a significant political shift in leadership that brought relief to the majority of that countries citizens (the best) but also encouraged the minority opinion to lash out with provocation from domestic actors and foreign states (the worst). This highlight the fact that digital security concerns reaches far beyond the confines of corporate CISO offices.
The rioters are extreme anti-immigration nationalists whipped up by false information regarding the stabbing of several young children and adults at a dance recital in Southport, a town just north of Wales. The disinformation came from several sources but is primarily coming through a Russian-linked website posing as a legitimate American news organization. The claim was meanwhile amplified up by far-right figures Tommy Robinson and Andrew Tate. Robinson was arrested under anti-terrorism laws but is out on bail has been vacationing in Europe. He is still spreading disinformation. Tate is currently under “judicial supervision” for rape and human trafficking charges. X owner Elon Musk has also participated personally in sewing the discord.
Foreign interference grows
Meanwhile, open source intelligence monitored by companies like Zero Fox and Fletch have identified efforts by North Korea and Russia to interfere in elections of Western countries including Germany and the United States. Zero Fox said, “The Telegram-based bot service IntelFetch had been aggregating compromised credentials linked to the Democratic National Committee (DNC) and their websites. This data, primarily sourced from botnet logs and third-party breaches, includes sensitive information such as login credentials for party members and delegates. This breach poses a significant risk of unauthorized access and potential disruptions to the convention.”
Zero Fox said the DNC had been alerted several weeks ago and that the weaknesses fixed. The DNC Convention is set to begin August 19 and Zero Fox was planning on announcing their findings that day to boost their profile.

Addressing Financial Organizations’ Digital Demands while Avoiding Cyber Threats
Keeping up with requirements has caused financial organizations to rapidly overhaul their IT infrastructure. Because of this rapid digitalization, organizations are consuming many different security solutions creating a bespoke environment that inadvertently exposes them to cyber threats.

The Crucial Role of Regulatory Frameworks in Ensuring Robust Cyber Security
In order to understand the ever-changing regulatory landscape, we spoke to eight cybersecurity experts about the latest developments and how businesses should navigate their way through.
Mining data is daunting but crucial
The cybersecurity industry seems addicted to research but isn’t all that good at it. Mining the massive amount of data produced is daunting but crucial to everyone.
Surveys and studies are an important part of marketing form the cybersecurity industry. Cyber Protection magazine receives a lot of them. We read them all. In the two months before the RSA Conference, more than one a day came into our inbox. However, they are not a great source of independent data and insight.
Ignoring the cherry-picked data highlighting a particular company’s product or service, there are a few nuggets that, taken together, produce some interesting insights. Out of 60+ reports, we took a pass on any that were repetitive, were suspect methodologically, or effectively plagiarized from another source. We chose to look at seven with a solid methodology, representation of industry-wide concerns, and originality. The reports came from Dynatrace, Black Kite, SlashNext, Metomic, Originality AI, Logicgate, and Sophos. We found three common themes: The impact of AI on security, government regulation compliance, and understanding of security concerns on the C-suites and board levels.
Understanding security issues.
Almost every study has a common complaint. CISOs say application security is a blind spot at the CEO and board levels. They say increasing the visibility of their CEO and board into application security risk is urgently needed to enable more informed decisions to strengthen defenses.
However, Dynatrace’s study said CISOs fail to provide the C-suite and board members with clear insight into their organization’s application security risk posture. “This leaves executives blind to the potential effect of vulnerabilities and makes it difficult to make informed decisions to protect the organization from operational, financial, and reputational damage.”
Recent news shows the study may have a point. Marriott Hotels admitted that a 2018 breach was the result of inadequate encryption of customer data. In 2018 the company claimed their data was protected by 128-bit AES encryption when customer identity was only protected by an outdated hashing protocol. One can imagine the discussion between the CEO and the IT department:
CEO: is our data encrypted?
IT manager: Yeah, sort of.
CEO: OK, good enough
If the CEO doesn’t understand the difference between a hash and AES encryption, that’s a problem.
And there many be evidence that ignorance is widespread. Apricorn reported that the number of encrypted devices in surveyed companies had dropped from 80 percent to 20 percent between 2022 and 2023. Some of that could be attributed to work-from-home (WFH) growth in companies. It is also likely that companies over-reported what was encrypted simply because they did not understand what “encryption” meant. Once they learned the meaning, adjustments were made.
That lack of a foundational security technology could be a reason for the devastating growth in ransomware in the past two years.

CTEM – useful or just another acronym?
CTEM is a term that was coined by Gartner (who else?) and is used to encapsulate an approach that seeks to assess and manage the exposure of the business on a continuous basis.