Holiday hunt for scalpers
The first sign of Christmas for Cyber Protection Magazine are warnings from cybersecurity companies about online shopping scams.…...
Read more...
The first sign of Christmas for Cyber Protection Magazine are warnings from cybersecurity companies about online shopping scams.…...
The Protector’s Edge: Leadership Through Strategy and Action is probably not a book on your Amazon wish list. That’s for good reason. It’s a dense book, more suited to a textbook, by one of the author’s own assertions, for Criminal Justice majors and special forces veterans. However, if you are a CEO, a CMO or a CISO, you might want to give it a skim.
Written by the security triumvirate of Chuck Randolph, Jonathan Wackrow, and Fred Burton, it provides an in-depth view of how professional personal protection work has morphed from the image of Kevin Costner in The Bodyguard to candidates for director of MI5.
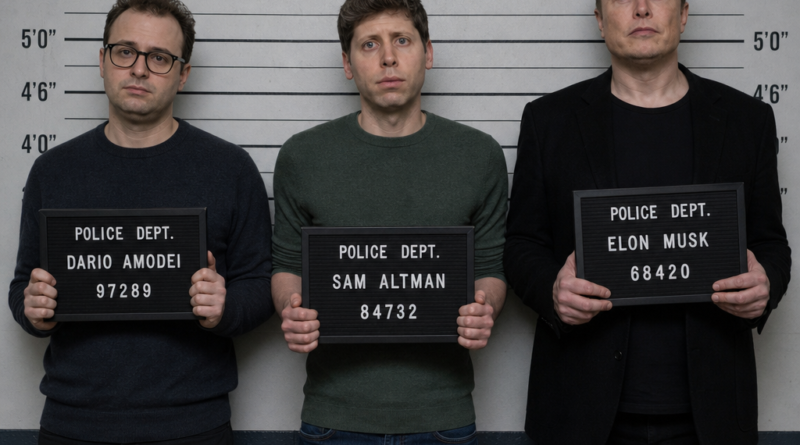
Regulating AI is a major issue in government halls worldwide, but legislators’ distinct lack of technical competence is hampering the effort. A less technical solution may exist. It has existed for more than a century; it requires little or no further legislation, and it could result in criminal charges against the CEOs of AI platforms.
(Note: senior executives at AI companies including Anthropic, Open AI and C3 AI were contacted for comment. None responded to the requests.)
TL;DR
License AI use like cars
Holding companies responsible
Groundwork already laid
Doctrine of reasonable care
Let’s begin with automotive use. Virtually every country requires licensing of drivers and registration of vehicles.
Read more...
We received a copy of Built Wrong by Richard Bird, CISO at Singulr AI, with a request for a review.…...
Is AI damaging collaboration between coders?
We put this question out to the cybersecurity community a few weeks ago and the simple answer to the question is yes and no. The breach of GitHub earlier this year did some damage to the platform, more reputation ally than functionally. Big users abandoned it for other Git platforms and usage has dropped dramatically over the ensuing months. The good news is the damage was identified in minutes and mitigated quickly, after putting the fear of god into developers.
What was less reported though were simultaneous attacks by the same hackers on virtually every popular developer operations (DevOp) platform. GitLab, not just GitHub, and BitBucket were hit at the same time. By July, Jira and Confluence were discovered compromised. GitHub claimed there was no degradation in uptime, but independent monitoring showed a decline to 86%. As a comparison, AWS’ S3 operates at 99.999999999% up time or “eleven nines”, while GitHub’s own reports show nine nines this year.
AI at the core
The impact of this change is entirely the result of AI use. The hackers employed customized AI agents, breached Github and stolen 3,800 of its internal repositories. They poisoned a popular VS Code extension called Nx Console, pushed the malicious version to the Visual Studio Marketplace, and let auto-update distribute it. The compromised version was live for just 18 minutes, but that was enough.
There has been a lot of discussion and debate over Anthropic’s watermark announcement, but it’s not much of an issue. It is required not only by the EU but China so AI companies must provide this technology. So for those who don’t like it, this is a chance to make lemonade out of lemons.
At Cyber Protection Magazine, we see some very positive aspects of this developing technology. We use AI in various ways: to automate the processing of junk… er, press releases, research purposes and identifying original content. While the AI industry like to promote the scare tactic of replacing humans, we see it as an efficiency tool, freeing us to do the work of covering cybersecurity news.
Hacking crews stole the private information of more than a million job seekers since 2022.…...

Black Hat USA kicked off over the weekend and company announcements followed the marketing focus on agentic AI products and services. However, there was more hash than corned beef in these announcements. Most were repackaged current product offerings.
A handful of announcements targeted at Black Hat focused on AI-generated or agentic threats. Most of the announcements repeated announcements prior to the RSA conference,for "agentic AI security" marketing. These include Tenable, Bedrock Data, Cycode, LimaCharlie, Flint AI, GTB Technologies, Strike48, Alice, Menlo Security and Adaptive Security.
Among more interesting legitimate announcements were Backslash Security, and Lineaje.
houlder surfing is probably the easiest security vulnerability to overcome, except to the companies selling solutions for it. In fact, there has been a lively debate CSO Online over whether those who buy a solution might not be intelligent enough to use digital tools.
The miasma of mendacity and misinformation in President Trump’s July address, showed he is at least as clueless about electionmore...