Focus Social Engineering – building the security mindset
Collaboration fueling configuration drift
Collaboration tools have fueled configuration drift facilitating phishing attacks since they became widespread during the COVID pandemic. The core of the problem is, as usual, human failure, or more accurately, human procrastination.
Configuration drift happens when vendors and customers join corporate networks with supposedly temporary credentials. When those credentials are not revoked quickly after the collaboration, system settings gradually, almost imperceptibly, diverge from a secure baseline state.
Collaboration tools, beginning with email in the 1970s, were largely clunky, on premises and limited to technically sophisticated organizations. Through the 20 years following the turn of the century they became more sophisticated and allowed inclusion of users outside the networks, like vendors, consultants, and customers. Approximately 400 to 600 million people in professional contexts today use Microsoft Teams, Slack, Google Workspace, Zoom, and dozens of others collaboration tools. Gartner said 90% of Fortune 500 companies standardize on Teams. Moreover, every team that uses collaboration tools configures every collaboration tool differently with no central enforcement.
“Configuration drift is one of the most under-recognized risks in modern cybersecurity,” said Garrett Hamilton, CEO and founder of Reach Security. “Security tools are constantly changing due to updates, new features, and operational adjustments. Over time, those changes create drift that quietly weakens defenses. Organizations need a continuous way to validate that the controls they depend on are still working as intended.”
That email from your bank looked real. That was the point
Brian Silverstein, May 29th 2026 Modern phishing has evolved rapidly with AI. It doesn’t come from strangers or an unknownmore
Haven free AI Security Companion protects from phishing
New AI-powered protection analyzes the context behind emails and browser activity to help users spot threats that traditional filters miss.
Scam bucket: 3-part scam sweeping nation
A multiphase scam is growing in the US, draining retirement accounts of US citizens, according to the FBI’s Internet Crimemore
Scam Bucket: Think before you click unsubscribe
You’ve done this many times. Checking your email you find a ton of spam, especially from this one organization or person. You are finally tired of it. You search the email for the “unsubscribe” link, buried somewhere on the bottom, and are about to click it.
STOP!

Phishing grows but can be blunted
Phishing attacks are on the rise again with the help of sophisticated generative-AI tools. However, new defenses and increased wariness among potential victims are blunting phishing’s potential for widespread harm.
Pig butchering: Proving the Luddites right
Pig-butchering may be proving the Luddites were right. The social-engineering scam bypassed ransomware as the most profitable cybercrime approximately two years ago. After government regulations and law enforcement took a big bite out of returns for ransomware this past year, public-private partnerships are taking aim at the new champ.
TL;DR
* Pig butchering eclipses losses from ransomware
* Top targets are tech savvy people under 50
* Human error trumps cyber awareness
* Public/private partnerships making inroads at dismantling scam operations
* Tips to avoid scams
* Podcast with Arkose CEO
Between 2020 and 20023, scammers reaped more than $75 billion from victims around the world. Approximately 90 percent of the losses came from of purchasing fraudulent cryptocurrency, according to the US Treasury Department’s, Financial Crimes Enforcement Center. In comparison, ransomware attacks in that same period harvested $20 billion worldwide in ransoms and cost approximately another $20 billion in recovery costs.
How Breach and Attack Simulation (BAS) Enhances Robust Cybersecurity Practices
Traditional methods of safeguarding information assets have become insufficient in today’s world of advanced cybercrime strategies. A more proactive approach is needed. This article explains the concept of breach and attack simulation (BAS).
The Evolution of Ransomware: From Simple Scams to Advanced Cybercrime Strategies
Ransomware vulnerability is typically exacerbated by immature security programs, leaving organizations susceptible to a variety of infiltration tactics. Additionally, a lack of security culture within companies increases susceptibility to ransomware attacks.
The Importance of Cybersecurity for Small Business
Small businesses face a myriad of cybersecurity threats, with ransomware and malware being the most prevalent. The consequences of such breaches can be profound and multifaceted, affecting various aspects of the business.
Cyberattack repercussions: dealing with the people perspective
Today’s organisations are all too aware of the potential financial, operational, and reputational costs posed by cybersecurity threats and the importance of fortifying defences and boosting their cyber resilience capabilities. And with good reason
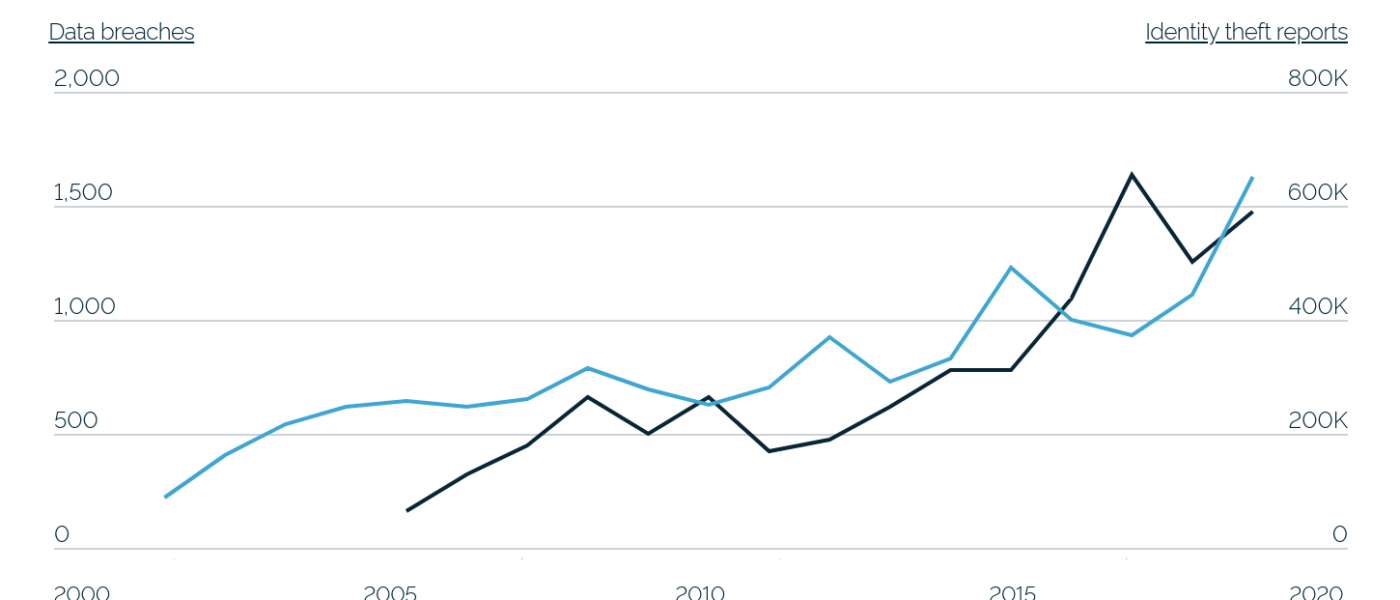
Do corporations really care about your security?
“Your security is important to us,” is a common phrase on corporate websites and emails, usually after some data breach that affects customers. To prove that statement, corporations invest billions of dollars in the cybersecurity industry. Most market projections say the industry is worth about $180 billion. About 15 percent of that market goes to data security. But all the indications are that we are losing the war in personal identity security That leaves is with the question: Do corporations really care about customer security?
Probably not
US Department of Health and Human Services reported recently that. in the US, there have been 2,213 breaches since 2020, with 152.1M affected individuals. That is almost half of the American population. But that is just breaches involving medical data.
The FBI reports, in the same period, more than 350 million stolen personal information records, exceeding the known population of the country. Worldwide, the number of personal identity information (PII) records exceeds one billion people.
So how bad is it? “I always tell people assume your social security number has been breached. Just assume that,” said John Meyer, senior director for Cornerstone Advisors, an organization providing security consultation to financial organizations.
So we are spending tens of billions of dollars to protect data from exfiltratation on almost a weekly basis from attacks bypassing current defenses. Is it worth the investment? Does protecting that data even matter?
Well, yes… sort of
Data security professionals say it is and it does. Communications, industry intellectual property, state secrets, and control of crucial systems must still be protected. Most professionals we talked to cite ransomware attacks as the primary reason for investing in security precuts and services.
Highly Effective AI-Enabled Cybersecurity Requires Massive Amounts of Data
Becoming an expert cybersecurity solution using AI requires processing and analyzing massive amounts of data over time to understand the nuances of how it’s being used for malicious purposes. Data, how it is collected, stored, and analyzed, and the insights gained are essential to successfully protecting, detecting, and responding to cybersecurity threats.
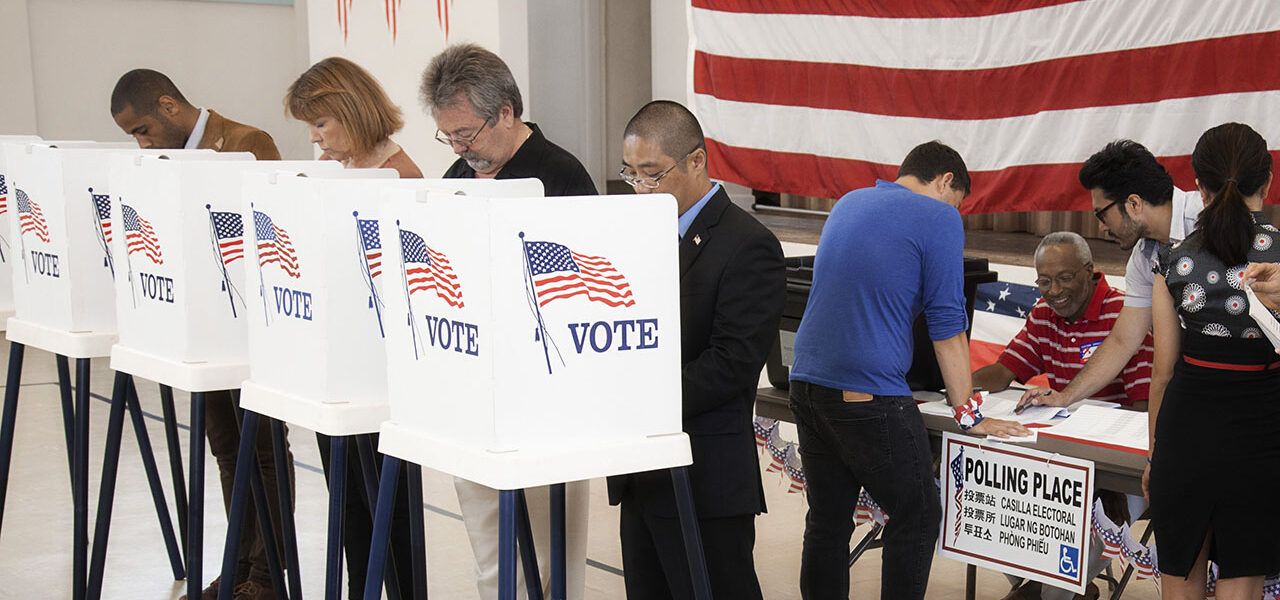
Election security is not a technology problem. It is how naive we are
When it comes to election security, the technology we use to vote and count those votes is not the problem. The problem is how naive we are.
Election security has been at the forefront of daily news cycles for more a decade. The concerns about illicit use of technology to input and count the votes turned out to be largely overblown. Every U.S. state other than the Commonwealth of Louisiana, uses paper ballots, matching the practice of every other western democracy. Lawsuits have bankrupted people and organizations claiming the technology was changing votes. Those that have complained the loudest about election interference are now facing prosecution for the crimes.
Now the tech focus is on the use of artificial Intelligence to create deepfake video and audio. A recent pitch from Surfshark,
Elder fraud festers out of control
As legislatures around the world try to get a handle on the growth of ransomware, another category of cybercrime is festering out of control: Elder fraud.
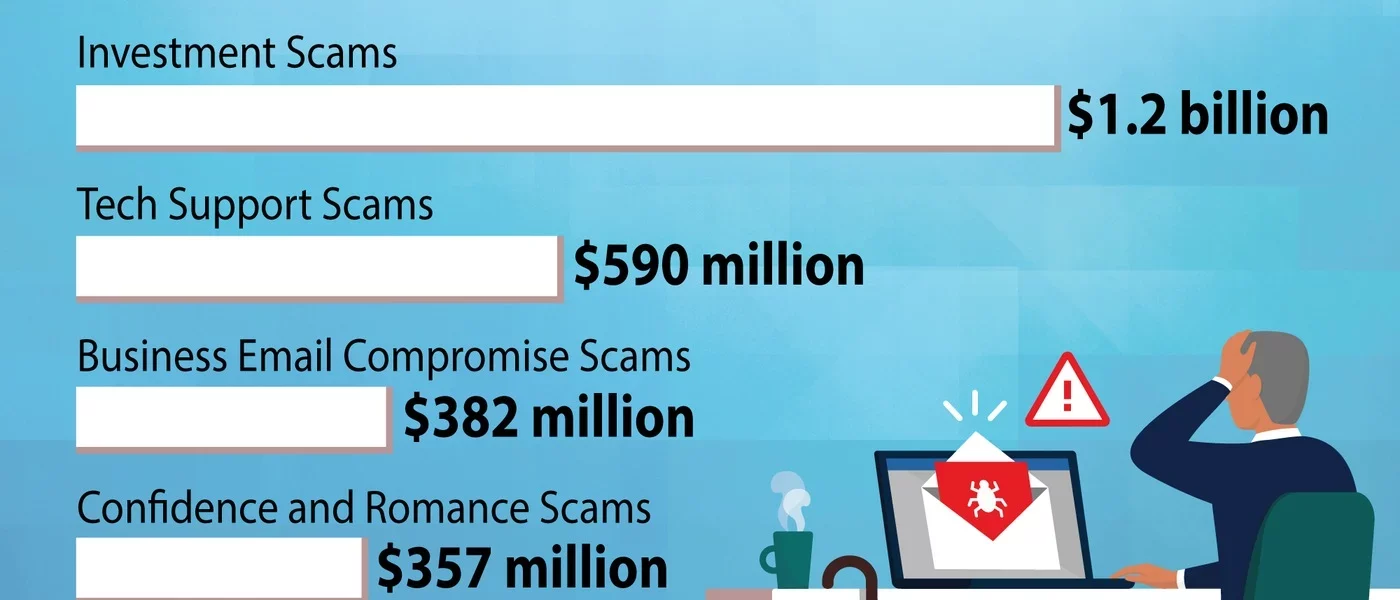
The FBI’s Internet Crime Complaint Center (IC3) reported more than 100,000 people in the US, 60 years and older, lost $3.4 billion total to digital scams. The IC3 pointed out that the elderly are half as likely to report a loss. So the actual crimes and losses are probably much higher.
In contrast, the total ransomware payouts last year from reporting companies was $1.1 billion according to Chainanalysis. While the total number of fraud reports to the IC3 appears to have leveled off after years of growth, elder fraud increased by 14 percent year on year.
“Combatting the financial exploitation of those over 60 years of age continues to be a priority of the FBI,” wrote FBI Assistant Director Michael D. Nordwall, who leads the Bureau’s Criminal Investigative Division, in the report. “Along with our partners, we continually work to aid victims and to identify and investigate the individuals and criminal organizations that perpetrate these schemes and target the elderly.”
Who is vulnerable?
Info-sec.live Weekly News Show with Rohit Ghai
Identity security is one of the most significant issues facing individuals and businesses. Phishing and identity theft dwarfs ransomware inmore
Reinforcing Multi Factor Authentication
As the password slowly abdicates to a new heir, which specific alternatives are shaping up to take its place? Multi-factor authentication (MFA) has been rapidly adopted by organizations to help reduce the opportunities for breaches. But MFA brings its own considerations that must be addressed.
Mining data is daunting but crucial
The cybersecurity industry seems addicted to research but isn’t all that good at it. Mining the massive amount of data produced is daunting but crucial to everyone.
Surveys and studies are an important part of marketing form the cybersecurity industry. Cyber Protection magazine receives a lot of them. We read them all. In the two months before the RSA Conference, more than one a day came into our inbox. However, they are not a great source of independent data and insight.
Ignoring the cherry-picked data highlighting a particular company’s product or service, there are a few nuggets that, taken together, produce some interesting insights. Out of 60+ reports, we took a pass on any that were repetitive, were suspect methodologically, or effectively plagiarized from another source. We chose to look at seven with a solid methodology, representation of industry-wide concerns, and originality. The reports came from Dynatrace, Black Kite, SlashNext, Metomic, Originality AI, Logicgate, and Sophos. We found three common themes: The impact of AI on security, government regulation compliance, and understanding of security concerns on the C-suites and board levels.
Understanding security issues.
Almost every study has a common complaint. CISOs say application security is a blind spot at the CEO and board levels. They say increasing the visibility of their CEO and board into application security risk is urgently needed to enable more informed decisions to strengthen defenses.
However, Dynatrace’s study said CISOs fail to provide the C-suite and board members with clear insight into their organization’s application security risk posture. “This leaves executives blind to the potential effect of vulnerabilities and makes it difficult to make informed decisions to protect the organization from operational, financial, and reputational damage.”
Recent news shows the study may have a point. Marriott Hotels admitted that a 2018 breach was the result of inadequate encryption of customer data. In 2018 the company claimed their data was protected by 128-bit AES encryption when customer identity was only protected by an outdated hashing protocol. One can imagine the discussion between the CEO and the IT department:
CEO: is our data encrypted?
IT manager: Yeah, sort of.
CEO: OK, good enough
If the CEO doesn’t understand the difference between a hash and AES encryption, that’s a problem.
And there many be evidence that ignorance is widespread. Apricorn reported that the number of encrypted devices in surveyed companies had dropped from 80 percent to 20 percent between 2022 and 2023. Some of that could be attributed to work-from-home (WFH) growth in companies. It is also likely that companies over-reported what was encrypted simply because they did not understand what “encryption” meant. Once they learned the meaning, adjustments were made.
That lack of a foundational security technology could be a reason for the devastating growth in ransomware in the past two years.

RSAC Reporter’s Notebook: Change is coming
The cybersecurity industry is just absolute chaos, and rightly so. This is the industry charged with plugging dikes during the Class-5 hurricane that the internet seems to be today. Nowhere is that chaos more evident than at RSAC just from a marketing perspective. Everyone has “ground-breaking”, “industry-leading”, and “first ever” product offerings and this year was no different. But if you can look past the Macho-man impersonations, Formula One cars, and the mesmerizing miasma of the website and show floor, you can see an order forming in the chaos. Change is coming.
Back to step one
RSA CEO Rohit Ghai, said we have missed a step in AI development. “We’ve seen it first as a co-pilot alongside of a human pilot and then see it taking over flying the plane.” He said the first step is making it an advanced cockpit making it easier for less trained and experienced people to do the work. He pointed out that cybersecurity is an industry with negative employment making it difficult to find experienced technicians to do the work.
Last year, any discussion of ethical development was met with confused stares. This year, the need for ethical AI development is taken seriously but few can see a profit in it. Cybersecurity VC Rob Ackerman (DataTribe) and Carmen Marsh, CEO of the United Cybersecurity Alliance, were open to suggestions,
“From the perspective of (companies like OpenAI), I understand the reasons to go as fast as they can to develop a true artificial intelligence, the question is, who are the people in the room guiding the process?” said Ackerman. “Once you get a diverse set of advisors working on the problem, then you do the best you can to create something ethical. But right now, we aren’t even doing the best we can.”
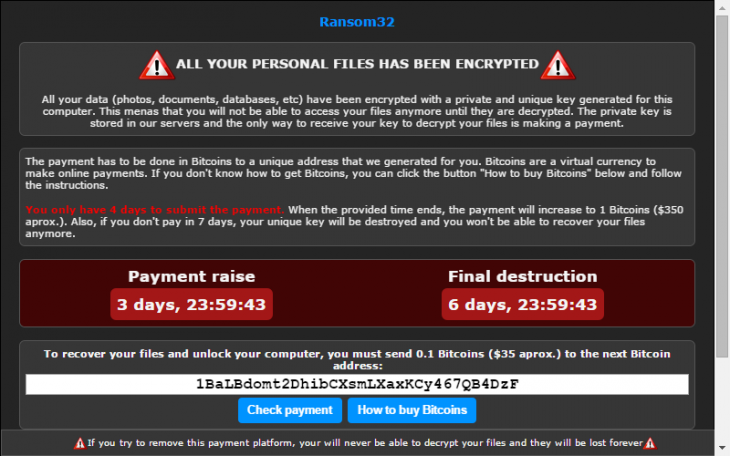
How to stop ransomware in its tracks
The name WannaCry still invokes memories of chaos and disaster amongst anyone in the technology world. The anniversary of this widespread attack in May each year has been named Anti-Ransomware Day, to encourage organisations to back up their data and adopt necessary security protections.